General Cybersecurity Statement by FENECON
1. Cybersecurity as a Prerequisite for the Energy Transition
A successful energy transition based on 100% renewable energy is hardly conceivable without a digital transformation of the energy system. However, as new digital possibilities emerge, so do greater demands on information security, data protection, and system resilience. That is why Heckert Solar consistently integrates cybersecurity into its products, processes, and strategic decisions.
2. Why Cybersecurity Is Especially Important in the Energy Sector
Energy supply is one of the most critical infrastructures in modern societies. As energy storage systems, inverters, energy management systems, wallboxes, and heat pumps become increasingly interconnected, the importance of secure and robust system architectures continues to grow.
The reality is that, according to estimates, approximately 80% of the inverters installed in Europe come from countries that are classified by the EU as high-risk. These devices are often permanently connected to cloud services in their countries of origin. With more than 117 GWp of installed photovoltaic capacity in Germany alone, this corresponds to a capacity of approximately 93 GW—more than 50 modern nuclear reactors, each with a capacity of approximately 1.6 GW.
2.1. The Specific Risks of Interconnected Energy Systems
As with any security or safety issue, there is no such thing as 100% protection; vulnerabilities and "weak points" can be hidden in any component. However, PV systems, battery inverters, and energy management systems are key components because they combine three unfavorable characteristics at the same time:
- Large quantities are deployed
-
Millions of identical devices a successful attack scales massively.
- They are controlling, not just measuring
-
They actively interact with the power grid (active power, reactive power, frequency support, active charging/discharging).
- They form a communication network
-
Cloud connection, remote maintenance, APIs, aggregators.
2.2. Market Comparison: Typical Battery Storage System
A standard battery storage system—consisting of a battery inverter, BMS, and battery modules—is structured as follows and typically uses the communication devices shown:
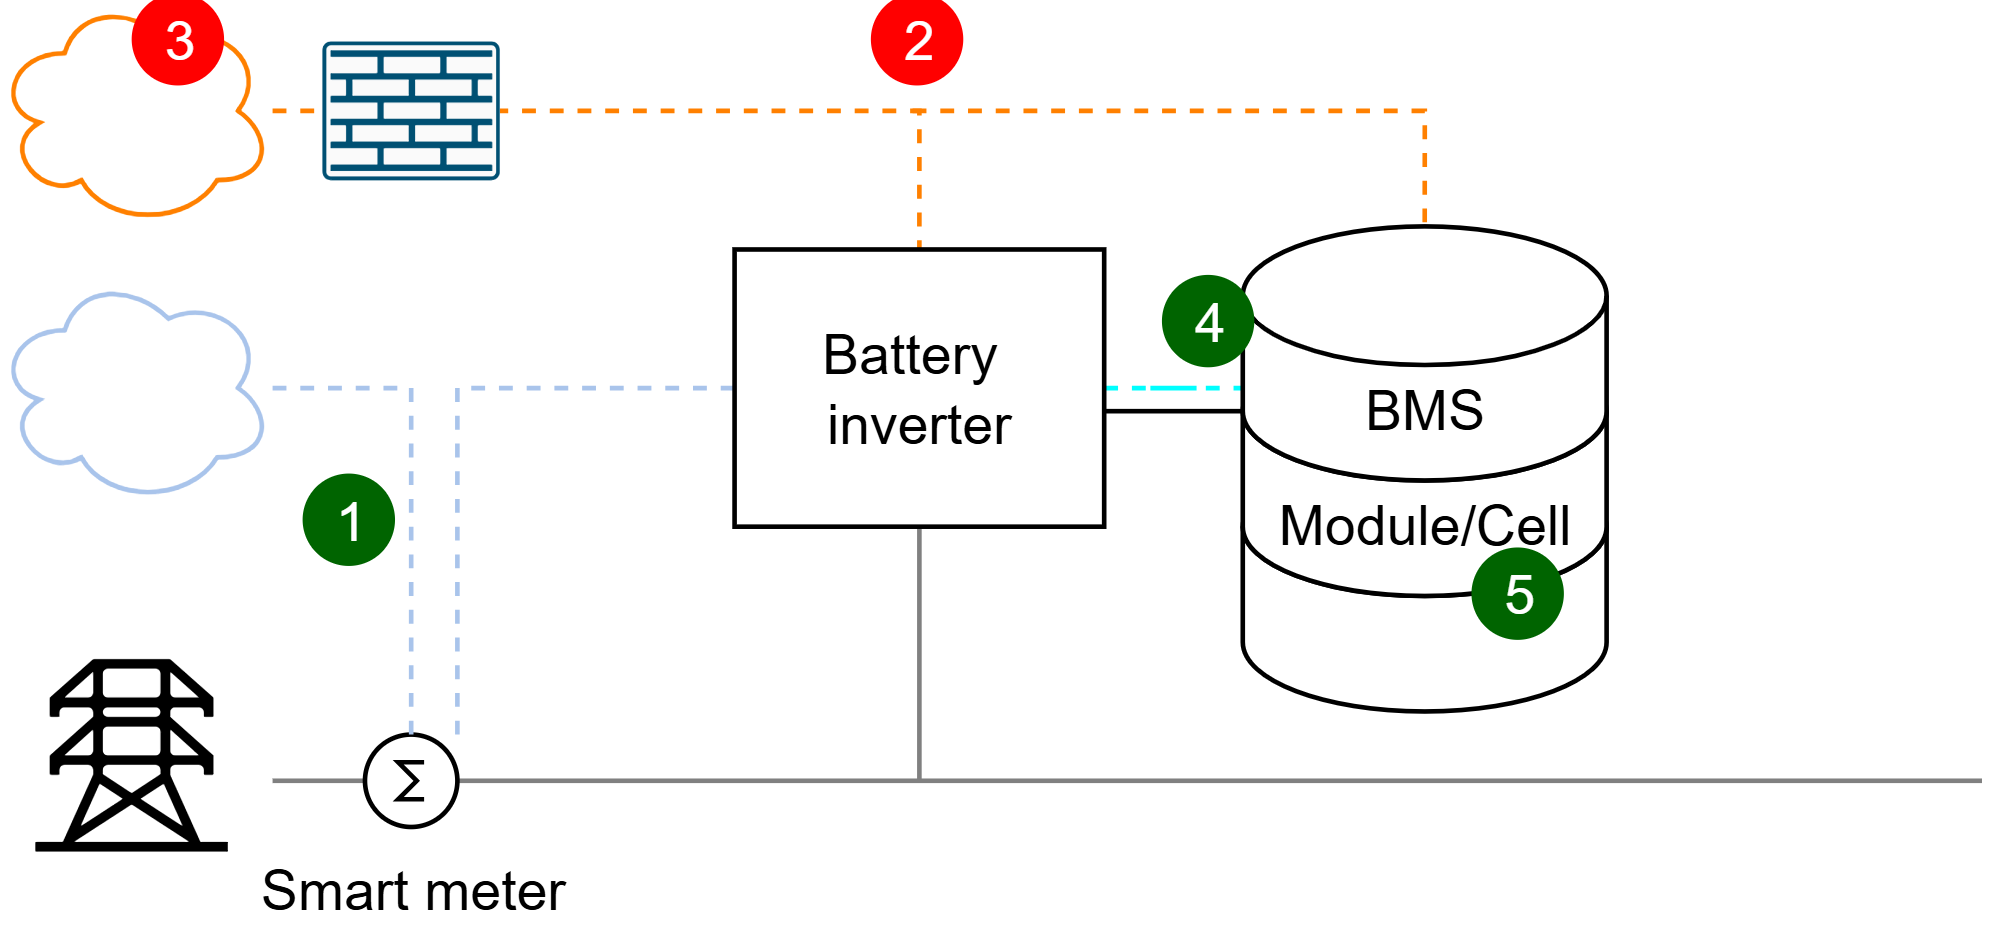
(1) BSI-compliant (Federal Office for Information Safety) communication and control via market communication, metering point operators, smart meter gateway infrastructure (SMGW), and the FNN control box:
-
Risk: low
(2) A permanent, bidirectional internet connection to the cloud of the inverter and/or BMS manufacturer:
-
For live monitoring, firmware updates, remote maintenance.
-
Advanced optimizations (artificial intelligence, forecasting, timetable, etc.) from the cloud.
-
Risk: high
(3) Manufacturer clouds are largely unregulated, without requirements such as KRITIS, ISO 27001, possibly NIS2, etc.
-
These servers are often located in China or the United States, or fall under their sphere of influence (e. g. Amazon Web Services (AWS), Microsoft Azure)
-
Risk: high
(4) Internal communication between components, not cloud-connected:
-
Risk: low
(5) Passive components such as battery cells/modules:
-
Risk: low
Depending on the intended use or system size, additional networked components may be required. For example, wallboxes and heat pumps in residential applications, hyperchargers in industrial settings, or cooling systems in outdoor battery storage systems. In such cases, there may be a similar risk of impact on the energy system if these devices are connected to unregulated manufacturer clouds.
2.3. Regulatory developments and increasing requirements
Regulatory requirements for the cybersecurity of interconnected energy systems are increasing significantly across Europe. With regulations such as the NIS2 Directive, the Cyber Resilience Act (CRA), the Radio Equipment Directive (RED), IEC 62443, and ETSI EN 303 645, information security, secure software development, vulnerability management, and transparency throughout the entire product lifecycle are increasingly subject to mandatory regulations.
At the same time, topics such as digital sovereignty, resilient supply chains, and the management of critical components are becoming increasingly important. Heckert Solar welcomes uniform European standards that promote security, transparency, traceability, and fair competition, thereby strengthening confidence in the digital energy transition.
3. The Heckert Solar Principle: Cybersecurity by Design
Cybersecurity by Design describes the fundamental security architecture of Heckert Solar energy storage systems. The goal is to minimize potential vulnerabilities right from the design stage, to ensure that critical functions can run locally, and to keep dependencies on external services to a minimum.
3.1. Security Architecture of Heckert Solar Products
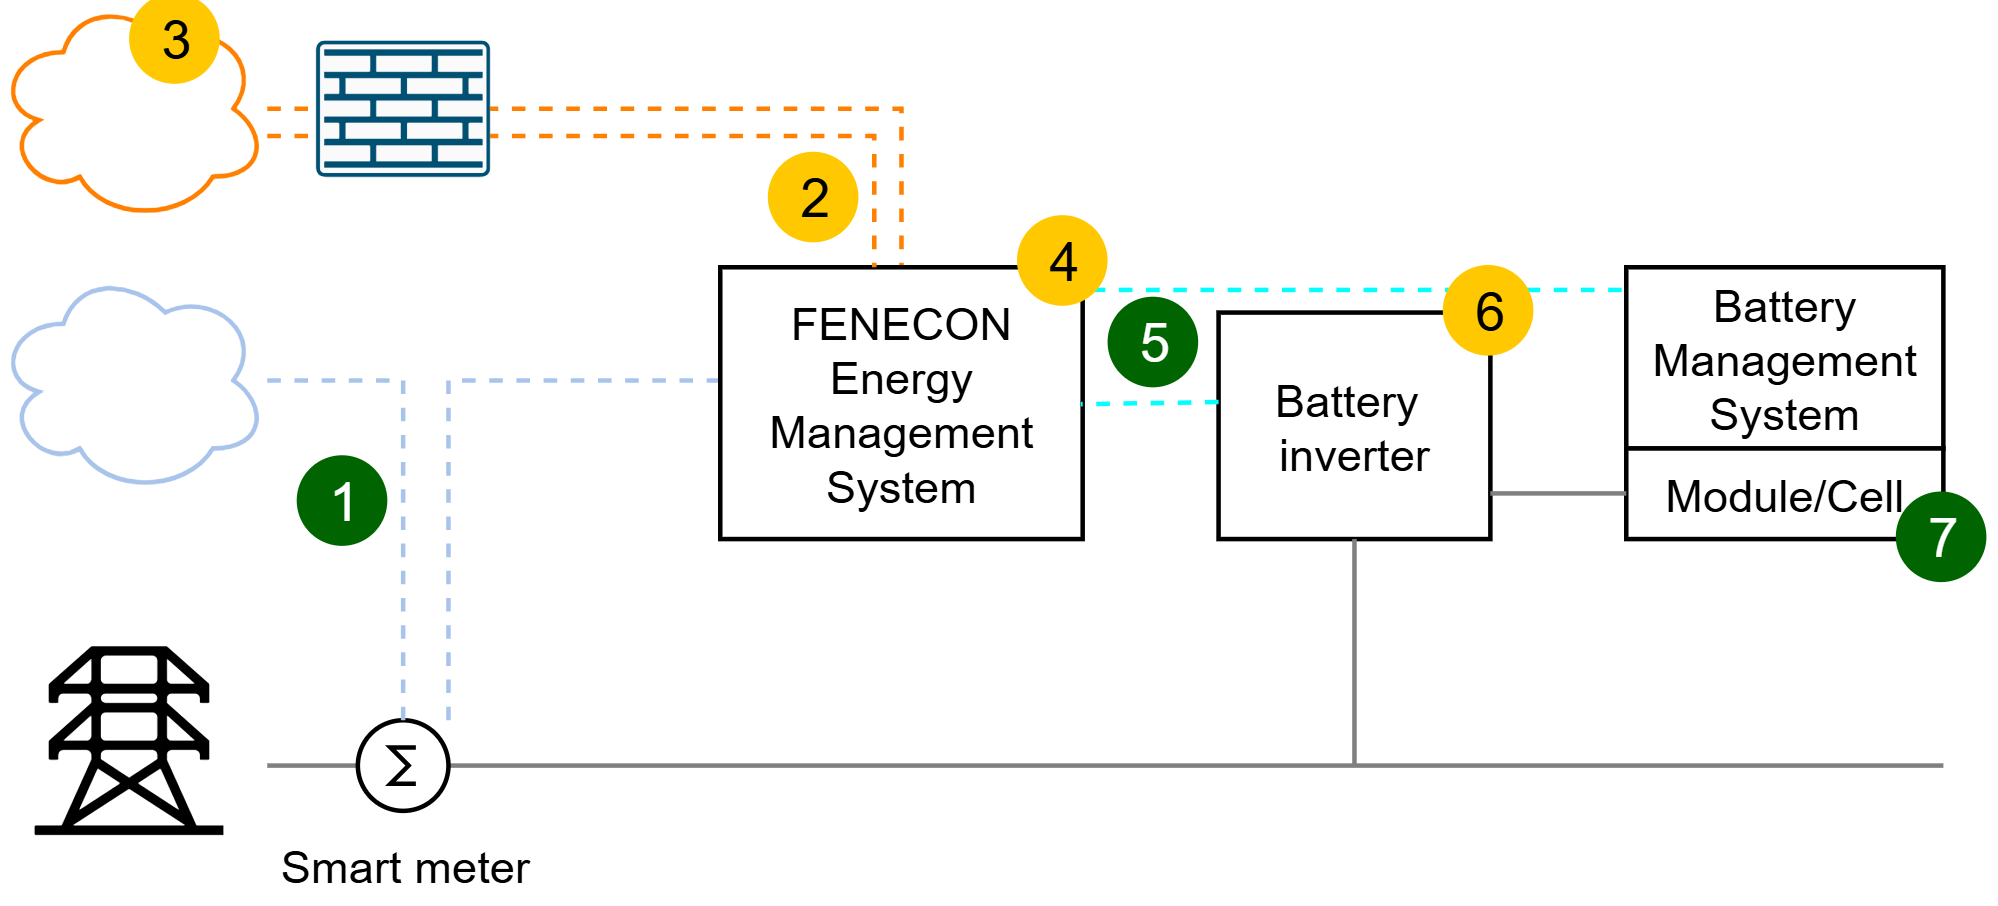
-
SMGW:
Processing of critical grid commands (e. g. dimming in accordance with § 14 a of the Energy Industry Act (EnWG), PV curtailment in accordance with § 9 of the Renewable Energy Sources Act (EEG)) by the energy management system and transmission to the battery inverter or other controllable consumer equipment.-
Risk: low
-
-
Permanent, bidirectional internet connection to the FENECON cloud:
-
For live monitoring, firmware updates (EMS, but also peripherals such as inverters and BMS), remote maintenance.
-
Separate connections to third-party services (e. g. weather forecast, electricity prices from ENTSO-E, Tibber, etc.) enable individual firewall releases.
-
Local AI models for forecasts and timetable optimization.
-
Risk: medium
-
-
-
FENECON cloud:
-
in ISO-27001-certified data centers in Germany with a German data center operator; German jurisdiction
-
Information security management system (ISMS) and reporting obligations in accordance with NIS2
-
Risk: medium
-
-
-
FEMS (FENECON Energy Management System):
-
developed as open source software together with the "OpenEMS — Open Energy Management System" project in Germany; auditable.
-
Permanent internet connection optional.
-
Risk: medium
-
-
-
Internal communication between non-cloud-connected components via physically separate networks:
-
e.g. depending on the system, separate Ethernet LAN/VLAN or serial communication (RS485)
-
Risk: low
-
-
-
Internal components from third-party providers:
-
Battery inverter from GoodWe (OEM with customized firmware) or Siemens/KACO, depending on the system
-
Battery management system, e. g. by Ampace/CATL/Würth
-
Possible attack vector: infected firmware updates; risk reduced by disconnecting from the network or internet connection
-
Risk: medium
-
-
-
Battery cells from China. Passive components without permanent internet connection:
-
Risk: low
-
3.2. Local Control and Operational Resilience
Connecting energy storage systems to the internet makes sense for many reasons. It enables active monitoring and supervision of the system even outside the local network. It also allows connection to external services—e. g. retrieving electricity prices—and facilitates quick service by the installer or manufacturer.
At the same time, it is precisely this internet connection that also creates vulnerabilities.
Cybersecurity by Design therefore means that an internet connection is always optional and that all functions must—as far as possible—work even without an internet connection: "Those who think offline also think defensively."
-
Reduction of Cloud Connections:
No components other than the FENECON Energy Management System (FEMS) are directly connected to the internet. -
Local AI Optimization and Algorithms:
All functions are generally available as a fallback even without a (permanent) internet connection. In this case, limitations may apply, e. g. to generation forecasts based on weather forecasts and to electricity market prices. -
Smart Meter Gateway (SMGW):
The official, BSI-compliant method for controlling controllable consumer equipment (German: SteuerVE) is implemented via the SMGW with the FNN control box.
3.3. Made in Germany
As a German company, we are subject to German liability law, German courts and German and European cybersecurity regulations (e. g. GDPR, NIS2, CRA)
In the event of a disaster, authorities have far-reaching access to companies — this reliability can only be practically implemented with German companies.
Buying from a German manufacturer like FENECON not only supports Germany as a business location with local added value, but also makes a direct contribution to internal and external safety and energy sovereignty.
3.4. Open Source
Source code auditing is an essential component of the compliance assessment for operators of critical infrastructure (KRITIS) pursuant to Section 8 a of the BSI Act (BSIG).
FENECON takes this a step further: by developing OpenEMS—together with a global community—as the “open-source operating system for the energy transition,” we are making a significant commitment to continuously improve the safety of the software in use.
-
"Closed source" means: "Trust us, we haven’t added anything."
-
Open source means: The source code is verifiable, security features are transparent, and backdoors cannot be hidden.
However, OpenEMS is not a monoculture; rather, it is designed so that various integrators can use it to build their own solutions. This leads to diversity among manufacturers, hardware, and operating models, and prevents the creation of a single point of failure or a central vulnerability.
"Isn’t open source insecure?"
Security vulnerabilities arise not from openness, but from a lack of testing.
4. Information Security at FENECON
As a German manufacturer that has been established in the German PV and energy market since 2011, has extensive experience with foreign components, and embraces open source in many ways, information security, data protection, and transparency are very important to us—not only in our products, but also within our company.
4.1. Certification of Our Processes and Measures
As part of our growth and professionalization strategy, we are actively pursuing official certification of our processes and measures.
-
ISO 9001:2015
TÜV-certified quality management for all German FENECON locations by TÜV Süd. (since 7 July 2025) -
ITQ Basic Audit
Initiation of a security process, including an audit and audit report, by an external IT service provider. (effective 11 June 2025) -
ISO 27001:2024
Certification is planned and being prepared.Monitoring and evaluating future relevant certifications under the Cyber Resilience Act (CRA), NIS2, and KRITIS — e. g.
-
ETSI EN 303 645 (EU Standard for Networked Devices)
-
RED 2014/53 (EU Standard for Cybersecurity)
-
IEC 62443 (Industrial communication networks - IT security for networks and systems)
-
-
Cloud Services
Hosting is provided exclusively in Germany, on our own servers and through an ISO 27001-certified hosting partner.
4.2. Corporate Strategy Initiatives
Information security is an integral part of FENECON’s corporate strategy. The goal is to continuously protect the availability, integrity, and confidentiality of information and to minimize risks to customers, partners, and the company.
4.2.1. Responsibilities and Governance
Overall responsibility for information security lies with Second Managing Director Stefan Feilmeier, who holds a bachelor’s degree in Business Informatics and a master’s degree in Computer Science (Embedded Systems).
To implement our corporate strategy in the area of information security, we use OKRs (Objectives and Key Results) and a delegation matrix.
The departments (e. g. IT, Quality Management, Corporate Governance, Facility Management, Strategy) work with their own staff and in collaboration with external experts to ensure long-term quality and continued development across the entire company.
4.2.2. ITQ Basic Test
The initial audit was conducted in early 2025 and lays the foundation for the Information Security Management System (ISMS). The audit covered the areas of management, IT, digital transformation and ERP systems, FEMS (FENECON Energy Management System), and marketing (e. g. website).
The audit covers the following areas: IT security management, antivirus protection, IT system safety, networking and the internet, VPN & Wi-Fi, content security, security requirements, patch management, passwords and encryption, emergency preparedness, data backup, infrastructure security, mobile devices, vendor management, mobile work, and the cloud.
The tasks identified in the audit were assigned to the relevant departments and are being monitored by a regular IT security task force.
4.2.3. Information Security Management System (ISMS)
Certification to ISO 27001:2024 is planned and currently in preparation. The actual work on this began in June 2025, following the successful ISO 9001:2015 audit. An ISMS manual is being developed, an external consulting firm has been engaged, and workshops have been scheduled.
4.2.4. Awareness and Training
Employees are regularly trained on cybersecurity and data protection through the internal e-learning platforms FENECON Academy and Sam Secova. Special attention is given to software and hardware developers, system administrators, and service technicians with elevated privileges.
4.2.5. Partnerships in Research and Development
FENECON has always worked closely with universities, research institutes, and industry peers. In particular, its collaboration within the OpenEMS Association e.V. and with the active open-source community surrounding OpenEMS—which serves as the foundation for FEMS—enables independent verification of software quality and code safety.
4.3. Continuous Improvement Over One-Time Measures
Cybersecurity is not a static state, but an ongoing process that is fully integrated into the development processes at FENECON. Updates for FEMS are released regularly, typically every two weeks. When vulnerabilities are discovered, there are clear reporting chains—and organizational mechanisms in place to quickly allocate development resources to address them. FEMS is developed and operated by a dedicated in-house team of software developers and DevOps engineers in Germany. Further developments and bug fixes are fully traceable through company-wide task management and source code versioning, unique identification of release versions, and clear changelogs.
This ensures that identified security vulnerabilities are addressed promptly.
5. Conclusion: Safety-Certified Energy Systems for a Resilient Energy Future
The energy transition requires not only high-performance systems, but also systems that are safe, transparent, and controllable. Cybersecurity, data protection, resilience, and digital sovereignty are essential prerequisites for this.
In essence: "Those who don’t build the technology don’t control it either."
-
Inverters and batteries are not just ordinary electrical devices; they are part of critical infrastructure.
-
If software, firmware, and update servers are not subject to European law, there is no real oversight.
-
A market that is 80 percent dependent on imports for critical technology is not a competitive market, but a potential risk.
-
Monocultures are: cheap to purchase—but expensive in a crisis.
-
No German power grid must be dependent on foreign servers.
As with any security or safety topic, there is no such thing as 100% protection; vulnerabilities and “design-in failure points” can be hidden in any component. No norm, standard, or certification will ever guarantee complete safety. FENECON relies on transparency (both as a company and in its products), regular updates, local oversight, and Made in Germany to minimize risks to end users, installers, the power grid, and society as much as possible.
Updated on 14.08.2026.